Anthropic-Cybersecurity-Skills: are there really 817 skills across 6 frameworks?
The claim“817 structured cybersecurity skills for AI agentsAI agent An AI that takes actions in steps (runs commands, edits files, browses) instead of only chatting. Glossary · Learn more, mapped to 6 frameworks (MITRE ATT&CK, OWASP, NIST and more)”
Live stats · checked
Review lives at rockytested.com · @RockyTested
 Counted. Useful? Not proven.
 Security
With vs without
No with-skill pass count is on file.
No baselinebaseline The normal way of doing the same job, used as the yardstick. Rocky compares every claim against a baseline on the same machine. Glossary pass count is on file.
Usefulness is a separate question from “does the repo exist.” It needs the same task run twice. Until that A/B is published, both cells stay blank.
Unproven -- head-to-head A/B test (same task with and without the skill loaded) is queued as Phase 2.
What the test plan says
Count every SKILL.md in the repo, check each has valid YAML frontmatter with a name and description, and count how many actually name a security framework. Pure static read, no code run.
Four verdicts
One stamp is not the whole story. Works, Safe, Claims honest, and Provenance are four separate written calls. A missing call stays “not tested yet.”
Phase 1 only counted and parsed. The with-vs-without A/B on ~100 skills is queued as Phase 2; until that lands, usefulness is not measured.
No confirmed malware in the surface scan, but two README-featured agents have confirmed bugs (memory-forensics TypeError; breach-containment clock-derived password + hardcoded CONTAINED). README funnels collect leads (survey with Casky Tokenstoken The small chunks a model reads and writes. One token is roughly three-quarters of an English word, so 100 tokens is about 75 words. Glossary · Learn more, casky.ai waitlist). Not a hard Safe fail yet — no confirmed secret exfil.
Claim ledger: 3 supported, 11 partly, 8 contradicted, 6 unverified. Contradictions include skill anatomy, token-cost claims, 'all 22 CSF categories', 'zero deprecated IDs', Navigator release assets, and 'production-grade' on sampled evidence.
Independent project with a buried non-affiliation disclaimer that does not travel into plugin.json / CITATION.cff / the GitHub description. Bulk history (611 skills in commitcommit One saved version of a repo's code. Rocky pins the exact commit so anyone can rerun the same code. Glossary · Learn more 1). Star-integrity sampling was blocked on our test box (environment limit, not a finding).
Safety is a hard cap. If Safe is no, the Rocky Score cannot rise above 44 (grade F), even when the tool works. A blank Safe card means not tested yet, not safe. How the four verdicts roll up →
| Claim part | Measured | Result |
|---|---|---|
| Finding 1 | The 818-skill count and the six frontmatter framework fields are real and machine-checked, and 364 of 366 framework IDs we validated exist in the official catalogs | measuring |
| Finding 2 | But counting files can't tell you whether a skill helps an agent, and the claim ledger logs 8 contradicted README claims -- so usefulness stays unproven until the A/B lab run | measuring |
What it is: A large bundle that claims 817 cybersecurity skills for AI agents, each tied to frameworks like MITRE ATT&CK and OWASP. Rocky counts them and checks the framework claim, rather than taking the number on faith. Claim source →

The 818-skill count and the six frontmatter framework fields are real and machine-checked, and 364 of 366 framework IDs we validated exist in the official catalogs. But counting files can't tell you whether a skill helps an agent, and the claim ledger logs 8 contradicted README claims -- so usefulness stays unproven until the A/B lab run.
⚠️ Read this before quoting the verdict
- Do not read UNPROVEN as fake: the structure claims largely hold (818 skills, six mapping fields, valid IDs). It means nobody -- including us, yet -- has measured whether these skills make an agent better.
- The claim ledger (data/claims/mukul975-cyber-skills.json) has 28 rows: 3 supported, 11 partly, 8 contradicted, 6 unverified. Contradicted items include the documented skill anatomy, the token-cost claims, 'all 22 CSF categories', 'zero deprecated IDs', and 'production-grade' on sampled evidence.
- Both scripts we hand-checked from the README's own examples have confirmed bugs: the showcase memory-forensics agent crashes on every full report run, and the breach-containment agent reports CONTAINED regardless of whether any action succeeded.
- Star-integrity sampling was blocked at the API level from our test box (verified blocked for a control repo too), so no account-age numbers exist either way.
Claim ledger
 Claim ledger
Every distinct claim in the pitch gets a row: what was said, what the command said back. 28 claims on the ledger: 3 supported, 11 partly, 8 contradicted, 6 not measured.
Every command was run from the root of a fresh clone pinned to the commit above. Statuses: supported | partly | contradicted | unverified.
- ✓ Supported
“818 skills (README badge, intro line, 'search all 818 skills').”
Result818 skill folders; 818 SKILL.md filesCommand behind itfind skills -mindepth 1 -maxdepth 1 -type d | wc -l; find . -name SKILL.md | wc -l📝 All 818 frontmatters parse (818/818 yaml.safe_load OK, 0 failures).
- ✕ Contradicted
“'817 skills' (README framework-coverage line and domain-table footnote; GitHub repo description).”
Result818Command behind itfind skills -mindepth 1 -maxdepth 1 -type d | wc -l📝 The README uses 817 and 818 in the same file (lines 47 and 187 vs 13, 27, 43). The GitHub description still says 817.
- ≈ Partly
“34 security domains; 'Counts come from the subdomain field in each skill's frontmatter.'”
Result46 distinct subdomain valuesCommand behind itpython3: parse frontmatter of all 818 SKILL.md, count distinct 'subdomain' values📝 The 34-row table only works by silently merging near-duplicate values (soc-operations 35 + security-operations 28 = 'SOC Operations 63'; identity-access-management 37 + identity-and-access-management 2 + identity-security 1 = 'IAM 40'; red-teaming 33 + red-team 2 = 35; and so on). Table sums to 817, not 818. The GitHub repo description says 29 domains; a 2026-03-21 commit message said 38.
- ≈ Partly
“6 framework mappings: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, MITRE D3FEND, NIST AI RMF, MITRE F3; coverage 805 / 804 / 93 / 139 / 97 / 94.”
Resultattack 806, csf 805, atlas 93, d3fend 139, ai_rmf 97, f3 94Command behind itpython3: count skills with non-empty mitre_attack / nist_csf / atlas_techniques / d3fend_techniques / nist_ai_rmf / mitre_f3 frontmatter📝 All six fields exist and four of six counts match exactly; ATT&CK and CSF are each one higher than claimed (one skill added after the README text). Separate from frontmatter, the skill body text name-drops 11 distinct frameworks (NIST 817, CIS 270, OWASP 110, PCI DSS 64, ISO 27001 14, ...), measured in lab job 14.
- ✕ Contradicted
“Validated against MITRE ATT&CK v19.1 (the latest release).”
Resultcurrent enterprise collection is version 20.0, modified 2026-10-13Command behind itcurl attack-stix-data enterprise-attack.json; read x-mitre-collection version📝 v19.1 is no longer latest. The README also contradicts itself: line 77 says v19.1 is current and mapped, line 298 still says 'ATT&CK v19 lands April 28, 2026' with mappings 'forthcoming'. The v19+ tactic split is real: the v20 bundle has TA0005 'Stealth' and TA0112 'Defense Impairment'.
- ≈ Partly
“Zero revoked or deprecated IDs; 290 distinct techniques (146 base + 144 sub) across Enterprise, ICS, Mobile.”
Result292 distinct IDs (148 base + 144 sub); 290 valid and current; 0 revoked; 2 deprecated (T0807 Command-Line Interface, T0853 Scripting, both ICS)Command behind itpython3: check all distinct mitre_attack IDs against enterprise/ics/mobile ATT&CK STIX bundles📝 Very close to the claim, but not zero deprecated, and the distinct count is 292 not 290.
- ✓ Supported
“805/817 skills carry a mitre_attack frontmatter list.”
Result806 of 818Command behind itpython3: count skills with non-empty mitre_attack frontmatter📝 Off by one on both sides of the fraction; same ratio.
- ≈ Partly
“Per-tactic skill counts (Initial Access 467, Persistence 444, Privilege Escalation 464, Stealth 442, ...).”
Resultrecomputed counts run 2-7% higher on every row (Initial Access 484, Persistence 465, Privilege Escalation 480, Stealth 458); ordering identicalCommand behind itpython3: map each skill's techniques to tactics via kill_chain_phases in the three ATT&CK v20 bundles, count skills per tactic📝 Consistent with a table generated at an earlier commit, not with invented numbers.
- ✕ Contradicted
“Skill mappings align to all 22 NIST CSF 2.0 categories and reference 106 subcategories.”
Result52 distinct subcategory IDs used, all valid; they span 19 of 22 categoriesCommand behind itpython3: validate all distinct nist_csf IDs against the NIST CPRT CSF 2.0 JSON export; count distinct categories📝 Every ID used is real (0 invalid), but coverage is 52 subcategories / 19 categories, not 106 / 22.
- ≈ Partly
“atlas_techniques carry MITRE ATLAS IDs (release 2026.07, 101 techniques + 77 sub-techniques).”
Result22 distinct ATLAS IDs used, all 22 exist in the official ATLAS data (version 5.6.0)Command behind itcurl mitre-atlas/atlas-data dist/ATLAS.yaml; check all distinct atlas_techniques IDs📝 IDs are valid. The '2026.07 release with 101+77 techniques' version claim could not be matched to the official data's own version label and stays unverified.
- ≈ Partly
“94 fraud-relevant skills mapped to MITRE F3; all 123 F3 v1.1 technique IDs verified against the upstream STIX bundle.”
Result94 skills have mitre_f3; they use 68 distinct technique IDs (34 F1xxx fraud-specific + 34 reused T1xxx)Command behind itpython3: count skills with a mitre_f3 frontmatter block and collect technique IDs📝 The 94 is exact. MITRE F3 itself is real (ctid.mitre.org/fraud/ serves 'MITRE Fight Fraud Framework'). The 'all 123 IDs verified' and the April 9, 2026 release-date detail stay unverified: we could not fetch the F3 STIX bundle from our test box.
- ✕ Contradicted
“Each skill costs ~30 tokens to scan (frontmatter only).”
Resultmedian 812 characters, roughly 200 tokens at 4 chars/tokenCommand behind itpython3: median frontmatter length across 818 SKILL.md📝 Off by about 7x. Even the shortest frontmatters exceed 30 tokens.
- ✕ Contradicted
“500-2,000 tokens to fully load a skill.”
Resultmedian 9,952 characters (~2,500 tokens); 90th percentile ~3,700 tokensCommand behind itpython3: median full SKILL.md length📝 The median skill already exceeds the claimed upper bound.
- ✕ Contradicted
“Every skill follows the documented layout: SKILL.md + references/standards.md + references/workflows.md + scripts/process.py + assets/template.md.”
Resultstandards.md 352/818, workflows.md 288/818, process.py 282/818, template.md 287/818; the actual dominant layout is scripts/agent.py 809/818 + references/api-reference.md 811/818, which the diagram never mentionsCommand behind itpython3: file-existence count per skill folder📝 The README's own example skill (performing-memory-forensics-with-volatility3) contains none of the four documented files: it has SKILL.md, SKILL.es.md, LICENSE, references/api-reference.md, scripts/agent.py.
- ≈ Partly
“Markdown body sections: When to Use, Prerequisites, Workflow, Verification.”
ResultWhen to Use 817, Prerequisites 818, Workflow 604, Verification 42; only 31 skills have all four. 124 use 'Validation Criteria' instead of 'Verification'Command behind itpython3: regex count of H2 headings across 818 SKILL.md📝 The first two sections are near-universal; the documented 'Verification' section exists in about 5% of skills.
- ✕ Contradicted
“818 production-grade cybersecurity skills.”
Resultthe README's flagship skill's agent.py crashes with a TypeError on every full report run (stores a string at line 125, indexes it as a dict at line 141); the breach-containment agent.py resets AD passwords to a clock-derived value it never records and hardcodes status CONTAINED into its report regardless of whether any action succeededCommand behind itread scripts of README-featured skills (see docs/cyber-skills-phase1.md section 6)📝 Contradicted on sampled evidence; marketing adjective. Broad usefulness remains unproven either way until the A/B run.
- ? Unverified
“Every skill encodes real practitioner workflows, not generated summaries.”
Result611 complete skills landed in the first commit (2026-02-25, 1,765 files, 280,648 insertions); 648 skill anatomies added in one commit; 548 descriptions rewritten in one commit; all 809 agent.py and 282 process.py are byte-unique (md5)Command behind itgit log --reverse; git show --name-only <first commit>; per-commit file counts📝 History is consistent with bulk generation; content uniqueness is real. No command can settle authorship intent, so this stays unverified. Quality itself is what Phase 2 A/B measures.
- ? Unverified
“The largest open-source cybersecurity skills library for AI agents.”
Resultcomparative claim; no single command settles itCommand behind itnone - ? Unverified
“Works with 26+ AI platforms.”
Result24 named platforms plus 'Any MCPMCP Model Context Protocol: a standard plug that lets AI assistants use outside tools and data (files, browsers, databases). Glossary · Learn more-compatible agent'Command behind itmanual count of platforms named in README 'Compatible platforms'📝 Compatibility is a Works question for the A/B phase; not tested in Phase 1.
- ≈ Partly
“Featured in awesome-agent-skills, awesome-ai-security, awesome-codex-cli, SkillsLLM, Openflows, NeverSight skills_feed.”
ResultVoltAgent/awesome-agent-skills, ottosulin/awesome-ai-security and RoggeOhta/awesome-codex-cli READMEs each mention the repo; skillsllm.com and openflows.org both serve dedicated pages for it; NeverSight/skills_feed was renamed to NeverSight/learn-skills.dev and its README does not mention the repoCommand behind itgh api repos/<list>/readme | base64 -d | grep -c mukul975; curl the two directory pages📝 5 of 6 confirmed. These are listings/directories, not endorsements or editorial coverage.
- ? Unverified
“Quotes from Hasan Toor (X) and fazal-sec (Medium).”
ResultMedium post blocked by Cloudflare from our test box; the X post was not fetchable at allCommand behind itcurl the Medium URL📝 Neither quote could be checked against its source.
- ✕ Contradicted
“An ATT&CK Navigator layer file is included in the v1.0.0 release assets.”
Resultall four releases (v1.0.0-v1.3.0) have empty asset listsCommand behind itgh api repos/mukul975/Anthropic-Cybersecurity-Skills/releases --jq '.[] | {tag, assets}'📝 A navigator layer does exist in the repo at mappings/attack-navigator-layer.json — wrong location claimed, not a missing artifact.
- ≈ Partly
“Releases table lists v1.0.0 (March 11, 2026) as the release.”
Resultfour releases exist: v1.0.0 2026-03-11, v1.1.0 2026-03-21, v1.2.0 2026-04-06, v1.3.0 2026-06-22Command behind itgh api .../releases📝 v1.0.0 date matches; the table omits three newer releases but the text does say to check the Releases page.
- ≈ Partly
“Independent community project, not affiliated with Anthropic PBC.”
Resultdisclaimer appears exactly twice, both in README.md (lines 35 and 463); zero occurrences in CITATION.cff, .claude-plugin/marketplace.json, index.json, or the GitHub repo descriptionCommand behind itgrep -rn 'affiliated' across repo top-level and metadata files📝 The disclaimer exists, but every machine-readable artifact that carries the 'Anthropic' name (plugin manifest named anthropic-cybersecurity-skills, citation title, catalog) ships without it. See provenance file for branding placement.
- ≈ Partly
“14 contributors.”
Result15 GitHub contributors; git log shows 23 distinct author name+email identitiesCommand behind itgh api 'repos/.../contributors?per_page=100' --jq length📝 Maintainer commits under two display names (mukul975 and Mahipal) resolving to the same GitHub account.
- ? Unverified
“Cybersecurity workforce gap hit 4.8 million unfilled roles in 2024 (ISC2).”
Resultexternal statistic, not checkedCommand behind itnone run against ISC2 source📝 Matches widely reported figures but we did not verify the primary source.
- ✓ Supported
“Responsible disclosure with 48-hour acknowledgment.”
Resultline 28: 'Initial acknowledgment: Within 48 hours'Command behind itgrep -n '48' SECURITY.md📝 The policy text exists; response-time behavior not tested.
- ? Unverified
“npx skills add mukul975/Anthropic-Cybersecurity-Skills works immediately.”
Resultinstall/run checks belong to the lab phaseCommand behind itnot run in Phase 1
🔍 Coverage: Not stated yet. Rocky only lists the parts a run actually checked.
⚗️ Unproven usefulness. Unproven -- head-to-head A/B test (same task with and without the skill loaded) is queued as Phase 2.
Rocky's take: good uses & where it will fail you
Good uses
 Good uses
- Building a broad security-skills library for an agentA security lead wiring up an AI agent wants wide coverage: 818 SKILL.md files exist, all 818 have valid frontmatter, so there's a real, structured set to pull from, not a half-finished stub.
- Compliance work needing multiple framework tagsA compliance analyst mapping controls can lean on this: NIST appears in 817 skills, CIS in 270, PCI DSS in 39 (plus 25 as 'PCI-DSS'), and ISO 27001 in 14.
- ATT&CK-aligned threat content for a SOCA SOC analyst wanting MITRE ATT&CK-mapped material gets real hits: 190 skills cite 'MITRE ATT&CK' directly, plus 65 more using the short 'ATT&CK' spelling.
- Fast sanity-check before trusting a repo's claimsSomeone deciding whether to bother with this repo can get an answer fast: the full count-and-validate check ran in about 6 seconds wall time.
Where it will fail you
 Where it will fail you
- Expecting only the advertised 6 frameworksA reader who takes the '6 frameworks' claim at face value and searches for exactly six will be confused: Rocky found 11 distinct frameworks named across the skills, not 6.
- Hunting for deep STRIDE or kill-chain coverageA threat modeler specifically wanting STRIDE content will be disappointed: only 1 skill mentions STRIDE, and Cyber Kill Chain appears in just 2.
- Assuming structure means good adviceA beginner who sees 818 of 818 files passing validation may assume the content itself is solid, but the check only confirms structure and framework names, not advice quality.
- Wanting ISO 27001-heavy materialA manager building an ISO 27001 training track will find thin coverage: only 14 of the skills reference ISO 27001, far fewer than NIST's 817.
🤖 Drafted by an AI model from Rocky's measured results only; every number was machine-checked against the test data. People in the examples are made up.
Where this repo comes from
 Where this repo comes from
Facts and numbers only, each from a recorded command (see docs/cyber-skills-phase1.md). No conclusions are drawn here.
From: gh api repos/mukul975/Anthropic-Cybersecurity-Skills; gh api search/issues; git log
History facts
- First commit 2026-02-25 10:47 (+0100): 1,765 files, 280,648 insertions, 611 complete skill folders, message 'Initial commit - 611 cybersecurity skills across all subdomains'.
- Five commits each touch 548-1,468 files (bulk adds/rewrites); the repo went 611 skills (Feb 25) to 818 (Jun 22) in four jumps.
- Commit c21af33 (2026-03-11) changed 622 per-skill LICENSE files from 'Copyright (c) 2025 Anthropic Agent Skills Contributors' to 'Copyright (c) 2025 Mahipal' (MIT text at the time; all per-skill licenses are Apache-2.0 at the pinned commit).
- The maintainer commits under two display names (mukul975, Mahipal) that resolve to the same GitHub account; CITATION.cff credits 'Jangra, Mahipal'.
- Stated domain count over time: 38 (commit message, 2026-03-21), 29 (current GitHub description), 34 (current README), 46 distinct subdomain values in frontmatter.
Star integrity
🚧 Blocked Stargazer-list endpoints (REST with star+json and GraphQL stargazers connection) returned 404/empty from our test box for this repo AND for a control repo (microsoft/markitdown), so account-age sampling and star-burst timing could not be measured. This is an environment limitation, not a finding about the repo. Only the aggregate counts above are available.
Commands tried
gh api 'repos/mukul975/Anthropic-Cybersecurity-Skills/stargazers?per_page=3' -H 'Accept: application/vnd.github.star+json' -> 404gh api graphql stargazers(first:3) -> totalCount 0, edges []same two calls against microsoft/markitdown -> identical 404/empty
Funding links in the repo
github: mukul975 · custom: paypal.me/mahipaljangra (from .github/FUNDING.yml)
Where the README sends you
- mahipal.engineer/survey — README badge (top) and dedicated GARS-2026 section
tracking:utm_source=github_badge|github_repo, utm_medium=readme, utm_campaign=gars2026
page title: “GARS-2026 Survey · Global Agentic AI Readiness Study”
📝 README offers '50 Casky Tokens' for completing it and says the study is supervised by SRH Berlin (not verified). Page fetched with GET only; no form submitted. - casky.ai — README badge + 'Try it on the Playground' section
tracking:utm_source=github, utm_medium=readme, utm_campaign=cohort_launch, anchor #waitlist
page title: “Casky — AI Security Investigation Platform”
📝 The playground link lands on a waitlist anchor. - skillsllm.com/skill/anthropic-cybersecurity-skills — Featured-in table
page title: “Anthropic-Cybersecurity-Skills - AI Agents on GitHub (34.6k★) | SkillsLLM” - openflows.org/currency/currents/anthropic-cybersecurity-skills/ — Featured-in table
page title: “Anthropic Cybersecurity Skills — Openflows” - star-history.dera.page — Star-history chart images in README
Name & disclaimer placement
- Repository name (Anthropic-Cybersecurity-Skills)
- README title, banner image alt text
- CITATION.cff title ('Anthropic-Cybersecurity-Skills')
- .claude-plugin/marketplace.json plugin name ('anthropic-cybersecurity-skills')
- index.json repository URL
- Historical per-skill LICENSE copyright line ('Anthropic Agent Skills Contributors', removed 2026-03-11)
- README.md line 35 ('independent, community-created project. Not affiliated with Anthropic PBC.')
- README.md line 463 ('Community project by @mukul975. Not affiliated with Anthropic PBC.')
- GitHub repo description
- CITATION.cff
- .claude-plugin/marketplace.json
- index.json
From: grep -rn -i 'affiliat|anthropic' across top-level and metadata files

The files are real and the framework IDs mostly check out. The pitch oversells: anatomy diagram doesn't match the tree, 'production-grade' doesn't survive the two showcase scripts Rocky opened, and the Anthropic name rides above a disclaimer that never makes it into the machine-readable manifests. Useful? Ask Phase 2 — counting isn't testing.
Results, charted
 Results, charted
Rocky draws these at build time from the run's own numbers. Hover or read the hidden table for exact values. Verdict colors: green holds, yellow stretched, red failed, teal measuring.
| Group | Series | Value (skills) |
|---|---|---|
| Skills | Claimed | 817 |
| Skills | Found | 818 |
| Skills | Valid frontmatter | 818 |
| Skills | Name a framework | 817 |
| Item | Value |
|---|---|
| NIST | 817 |
| CIS | 270 |
| MITRE ATT&CK | 255 |
| D3FEND | 141 |
| OWASP | 110 |
| PCI DSS | 64 |
| ISO 27001 | 14 |
Score
 Score
The dial stays open on purpose. Usefulness has not been proven in a with-and-without run, so there is no letter grade. Subscores that were actually measured are on the right. Empty subscores stay “not measured”.
Partial rollup of the measured subscores only: 88. Not a Rocky Score and not a grade. It is not used to rank this review.
Graded on 50 of 100 weight points. Parts marked “not measured” are left out of the math, not counted as zero.
Medium confidence: claim test with one run per setup. How scores work. Scores only use measured results; parts Rocky didn't measure show as “not measured” and don't count.
Retest history
Testing ends when the run ends. If the repo ships a new version with a bold new claim, or newer models make a fair rematch possible, Rocky reruns the same test packet and the new result lands here next to the old one, so you can compare versions and models side by side.
Rerun it yourself
 Rerun it yourself
📦 When the test is done, the exact scripts, raw results and a copy-paste prompt for your own AI agent will appear here.
Repo & thanks
- Anthropic-Cybersecurity-Skills: 817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3 (Fight Fraud) · agentskills.io standard · Works with Claude Code, GitHub Copilot, Codex CLI, Cursor, Gemini CLI & 20+ platforms · 29 security domains · Apache 2.0 Built by @mukul975. Thank you!
Where the claim was posted

Equips AI agents with 818 structured cybersecurity skills mapped across six major frameworks, enabling senior-level security analysis within coding assistants. https://github.com/mukul975/Anthropic-Cybersecurity-Skills
Counts as of (Rocky's last check)
Where else this repo is talked about
On X: 19 posts linking the repo
Posts from to , in 6 languages. Checked . Found with X search for links to the repo; more may exist. Oldest first:
- Earliest we found @youyuy88 At first glance, you might think this repository was released by Anthropic. The author is mukul975, and it is a community directory. It has more than eight hundred skills and uses the agentskills io format. I only looked through the headings for hunting, response, forensics, and cloud security; offensive entries are also included, but I did not open them. It can be installed in Claude Code, Cursor, and Codex. Load it only with authorization. 🔗打开仓库第一眼会以为是 Anthropic 发的。 作者是 mukul975,社区目录。skill 八百多,格式走 agentskills io。我只翻过狩猎、响应、取证、云安全这几类标题;偏进攻的条目也在,没往下点。 Claude Code、Cursor、Codex 能装。有授权再加载。 🔗❤️ 21 · 🔁 3 · 📊 1.7K open
- @Jayson_security Anthropic-Cybersecurity-Skills: 818 structured cybersecurity skills for AI agents, mapped to MITRE ATT&CK, NIST, and more. Source:Anthropic-Cybersecurity-Skills: 818 habilidades estructuradas para agentes de IA en ciberseguridad, mapeadas a MITRE ATT&CK, NIST y más. Fuente:❤️ 1 · 🔁 0 · 📊 23 open
- @okattm (link only)❤️ 0 · 🔁 0 · 📊 7 open
- @srmarcmayol 817 cybersecurity skills for agents, across 29 domains, mapped to MITRE ATT&CK, NIST CSF, or D3FEND. The key: the agent follows the procedure of a senior analyst instead of improvising. Note: it is not from Anthropic and includes offensive techniques.817 skills de ciberseguridad para agentes, en 29 dominios, mapeadas a MITRE ATT&CK, NIST CSF o D3FEND. La clave: el agente sigue el procedimiento de un analista senior en vez de improvisar. Ojo: no es de Anthropic y trae técnicas ofensivas.❤️ 0 · 🔁 0 · 📊 28 open
- @noahxche @tumifuego all you need❤️ 1 · 🔁 0 · 📊 27 open
- @GYLQ520 At first glance, you might think this repository was released by Anthropic. The author is mukul975, and it is a community directory. It has more than eight hundred skills and uses the agentskills io format. I only looked through the headings for hunting, response, forensics, and cloud security; offensive entries are also included, but I did not open them. It can be installed in Claude Code, Cursor, and Codex. Load it only with authorization. 🔗打开仓库第一眼会以为是 Anthropic 发的。 作者是 mukul975,社区目录。skill 八百多,格式走 agentskills io。我只翻过狩猎、响应、取证、云安全这几类标题;偏进攻的条目也在,没往下点。 Claude Code、Cursor、Codex 能装。有授权再加载。 🔗❤️ 2 · 🔁 0 · 📊 261 open
All 19 posts, oldest first
- Earliest we found @youyuy88 At first glance, you might think this repository was released by Anthropic. The author is mukul975, and it is a community directory. It has more than eight hundred skills and uses the agentskills io format. I only looked through the headings for hunting, response, forensics, and cloud security; offensive entries are also included, but I did not open them. It can be installed in Claude Code, Cursor, and Codex. Load it only with authorization. 🔗打开仓库第一眼会以为是 Anthropic 发的。 作者是 mukul975,社区目录。skill 八百多,格式走 agentskills io。我只翻过狩猎、响应、取证、云安全这几类标题;偏进攻的条目也在,没往下点。 Claude Code、Cursor、Codex 能装。有授权再加载。 🔗❤️ 21 · 🔁 3 · 📊 1.7K open
- @Jayson_security Anthropic-Cybersecurity-Skills: 818 structured cybersecurity skills for AI agents, mapped to MITRE ATT&CK, NIST, and more. Source:Anthropic-Cybersecurity-Skills: 818 habilidades estructuradas para agentes de IA en ciberseguridad, mapeadas a MITRE ATT&CK, NIST y más. Fuente:❤️ 1 · 🔁 0 · 📊 23 open
- @okattm (link only)❤️ 0 · 🔁 0 · 📊 7 open
- @srmarcmayol 817 cybersecurity skills for agents, across 29 domains, mapped to MITRE ATT&CK, NIST CSF, or D3FEND. The key: the agent follows the procedure of a senior analyst instead of improvising. Note: it is not from Anthropic and includes offensive techniques.817 skills de ciberseguridad para agentes, en 29 dominios, mapeadas a MITRE ATT&CK, NIST CSF o D3FEND. La clave: el agente sigue el procedimiento de un analista senior en vez de improvisar. Ojo: no es de Anthropic y trae técnicas ofensivas.❤️ 0 · 🔁 0 · 📊 28 open
- @noahxche @tumifuego all you need❤️ 1 · 🔁 0 · 📊 27 open
- @GYLQ520 At first glance, you might think this repository was released by Anthropic. The author is mukul975, and it is a community directory. It has more than eight hundred skills and uses the agentskills io format. I only looked through the headings for hunting, response, forensics, and cloud security; offensive entries are also included, but I did not open them. It can be installed in Claude Code, Cursor, and Codex. Load it only with authorization. 🔗打开仓库第一眼会以为是 Anthropic 发的。 作者是 mukul975,社区目录。skill 八百多,格式走 agentskills io。我只翻过狩猎、响应、取证、云安全这几类标题;偏进攻的条目也在,没往下点。 Claude Code、Cursor、Codex 能装。有授权再加载。 🔗❤️ 2 · 🔁 0 · 📊 261 open
- @GYLQ520 At first glance, you might think this repository was released by Anthropic. The author is mukul975, and it is a community directory. It has more than eight hundred skills and uses the agentskills io format. I only looked through the headings for hunting, response, forensics, and cloud security; offensive entries are also included, but I did not open them. It can be installed in Claude Code, Cursor, and Codex. Load it only with authorization. 🔗打开仓库第一眼会以为是 Anthropic 发的。 作者是 mukul975,社区目录。skill 八百多,格式走 agentskills io。我只翻过狩猎、响应、取证、云安全这几类标题;偏进攻的条目也在,没往下点。 Claude Code、Cursor、Codex 能装。有授权再加载。 🔗❤️ 0 · 🔁 0 · 📊 106 open
- @xeonai44 Found this for cyber security skills❤️ 2 · 🔁 0 · 📊 50 open
- @xeonai44 @Teknium btw I found these skills for cyber security audit❤️ 2 · 🔁 0 · 📊 15 open
- @Dinosn The largest open-source cybersecurity skills library for AI agents❤️ 746 · 🔁 170 · 📊 41K open
- @tom_doerr Equips AI agents with 818 structured cybersecurity skills mapped across six major frameworks, enabling senior-level security analysis within coding assistants.❤️ 197 · 🔁 36 · 📊 12K open
- @NeoteoCom 818 cybersecurity skills for Claude Code: senior security analysis inside your coding assistant, mapped to six frameworks.818 skills de ciberseguridad para Claude Code: análisis de seguridad senior dentro de tu coding assistant, mapeados a seis frameworks.❤️ 0 · 🔁 0 · 📊 126 open
- @t1gerxt1ger A collection of security skills for AI has been released. • 818 skills, 34 domains, support for 6 frameworks • Intended for use in authorized environmentsAI 向けのセキュリティ・スキル集が公開。 ・818 スキル、34 領域、6 フレームワーク対応 ・許可された環境での利用が前提❤️ 0 · 🔁 0 · 📊 14 open
- @hemran_7282 Equips AI agents with 818 structured cybersecurity skills mapped across six major frameworks, enabling senior-level security analysis within coding assistants. #CyberSecurity #InfoSec #e0xsecops #TechLeadershi❤️ 0 · 🔁 0 · 📊 5 open
- @HackerOx26 Anthropic security Skills: #Anthropic #Security❤️ 0 · 🔁 0 · 📊 16 open
- @RangerCov_175 Most agent skills are vibes. These are mapped to MITRE ATT&CK. 817 files. Each one ties a specific capability to a framework ID. You get structure, not just prompts.❤️ 0 · 🔁 0 · 📊 57 open
- @laogeai 😤 Security checks rely on people following checklists, and you do not know what was missed. This repository organizes 817 security skills in an agent-usable format, aligned with 6 major frameworks, for direct use by AI. Thirty-four thousand stars.😤 安全检查靠人对清单,漏了不知道。这个仓库把 817 条安全技能整理成 agent 可用格式,对齐 6 个主流框架,挂给 AI 直接用。三万四千星。❤️ 0 · 🔁 0 · 📊 13 open
- @ngnicky The largest open-source cybersecurity skills library for AI agents 818 practitioner-grade cybersecurity skills · 34 security domains · 6 framework mappings · 26+ AI platformsAI 에이전트를 위한 최대 규모의 오픈 소스 사이버 보안 기술 라이브러리 818개의 실무급 사이버 보안 기술 · 34개의 보안 영역 · 6개의 프레임워크 매핑 · 26개 이상의 AI 플랫폼❤️ 22 · 🔁 5 · 📊 1.3K open
- @mobileossfinds (link only)❤️ 1 · 🔁 0 · 📊 9 open
Ran it yourself?
Share your rerun
- Download the rerun bundle above.
- Run it, or paste the prompt into your AI agent.
- Post your
results.json(a gist is fine) and reply to @RockyTested with the link.
Rocky reruns or spot-checks every submission before it counts. Verified reruns will appear here with your handle.
🏅 Helper leaderboard
No verified reruns yet. Be the first!
Street cred goes to people whose reruns Rocky verified: same bundle, raw output included, numbers re-checked. How it works
Badge & stat card
Put the verdict badge in a README or post. It always links back to the measured results.
[](https://rockytested.com/reviews/mukul975-cyber-skills/)
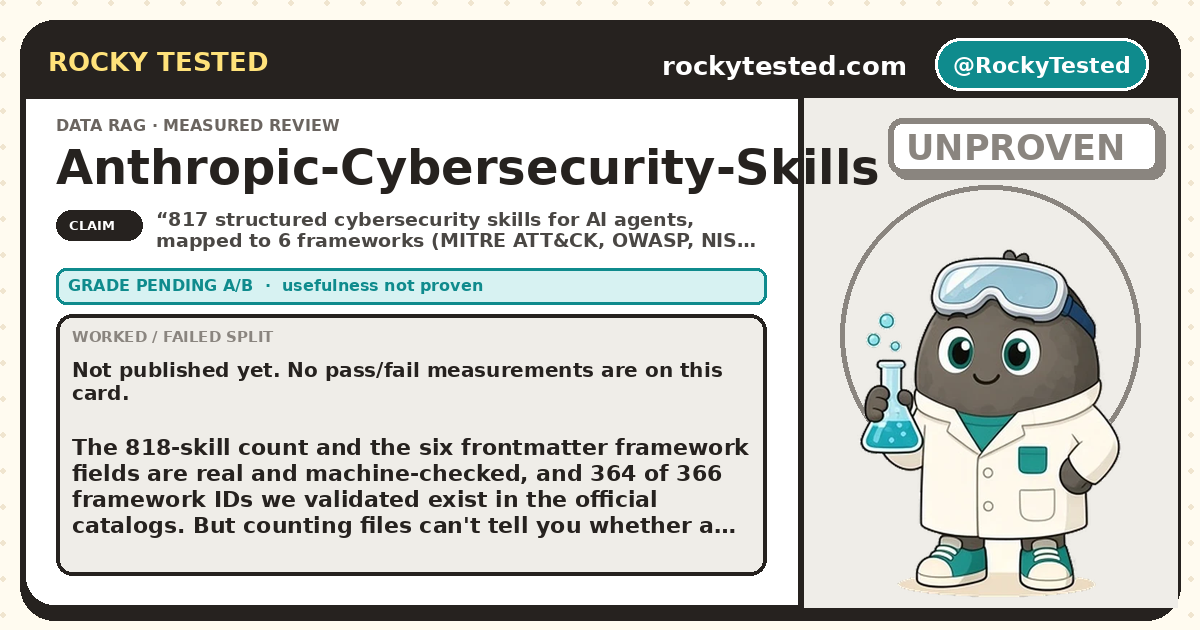
Stat card (1200×630). This is what shows up when the review is shared on X.
Machine-readable: /v1/reviews/mukul975-cyber-skills · Words with a dotted underline have a quick explanation: hover or tap. Glossary